Revolutionize your identityand access management
A cutting-edge IAM platform that prioritises business risk, ensures compliance and boosts efficiency. Achieve 95%+ coverage of permission models and automate 85% of access requests end to end.
SOC-2 Type II, PIPEDA and GDPR compliant
The Challenges of Sub-Optimal IAM
Manual and inefficient Identity & Access Management processes expose organisations to significant risks.
Data Breaches
Excessive access permissions lead to costly leaks, like Equifax and Capital One.
Fraud & Compliance
Weak Segregation of Duties (SoD) and trailing permissions increase fraud vulnerability.
Costly Audits
Manual processes result in time-consuming audits with persistent deficiencies.
Poor User Experience
Slow, manual access provisioning frustrates employees and hinders productivity.
“Nearly every significant cyber breach in recent years has been due to a failure to control privileged access”
Identity and access management, adapted to your business risks
The cornerstone of a strong cybersecurity programme is efficient and comprehensive identity and access management.
Automated identity lifecycle
Automated management of employee identity and access across the whole employee lifecycle — arrival, transfer, departure — so entitlements track the organisation as it changes.
- Joiners provisioned from the HR record, not a ticket.
- Movers reassessed on transfer, so permissions do not accumulate.
- Leavers de-provisioned across every connected application.
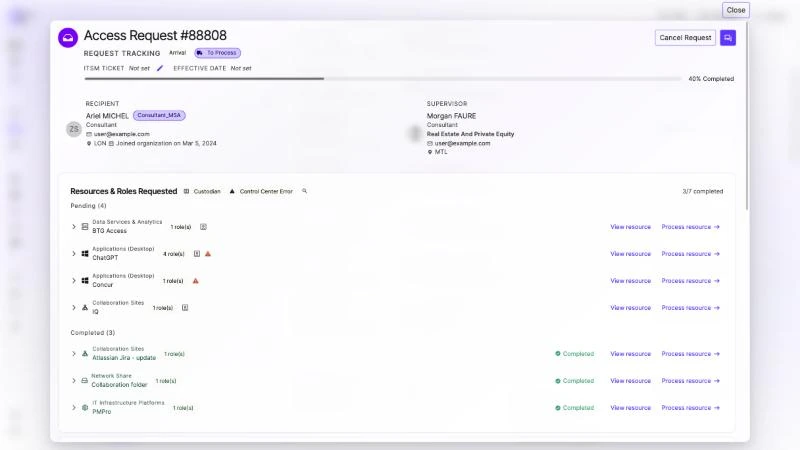
Self-service access request
Self-service access requests across all applications and resources, with configurable authorisation workflows that route each request to the people who can actually judge it.
- One catalogue covering every connected application and resource.
- Authorisation workflows configured per application, per risk level.
- Full audit trail and SLA management on every request.
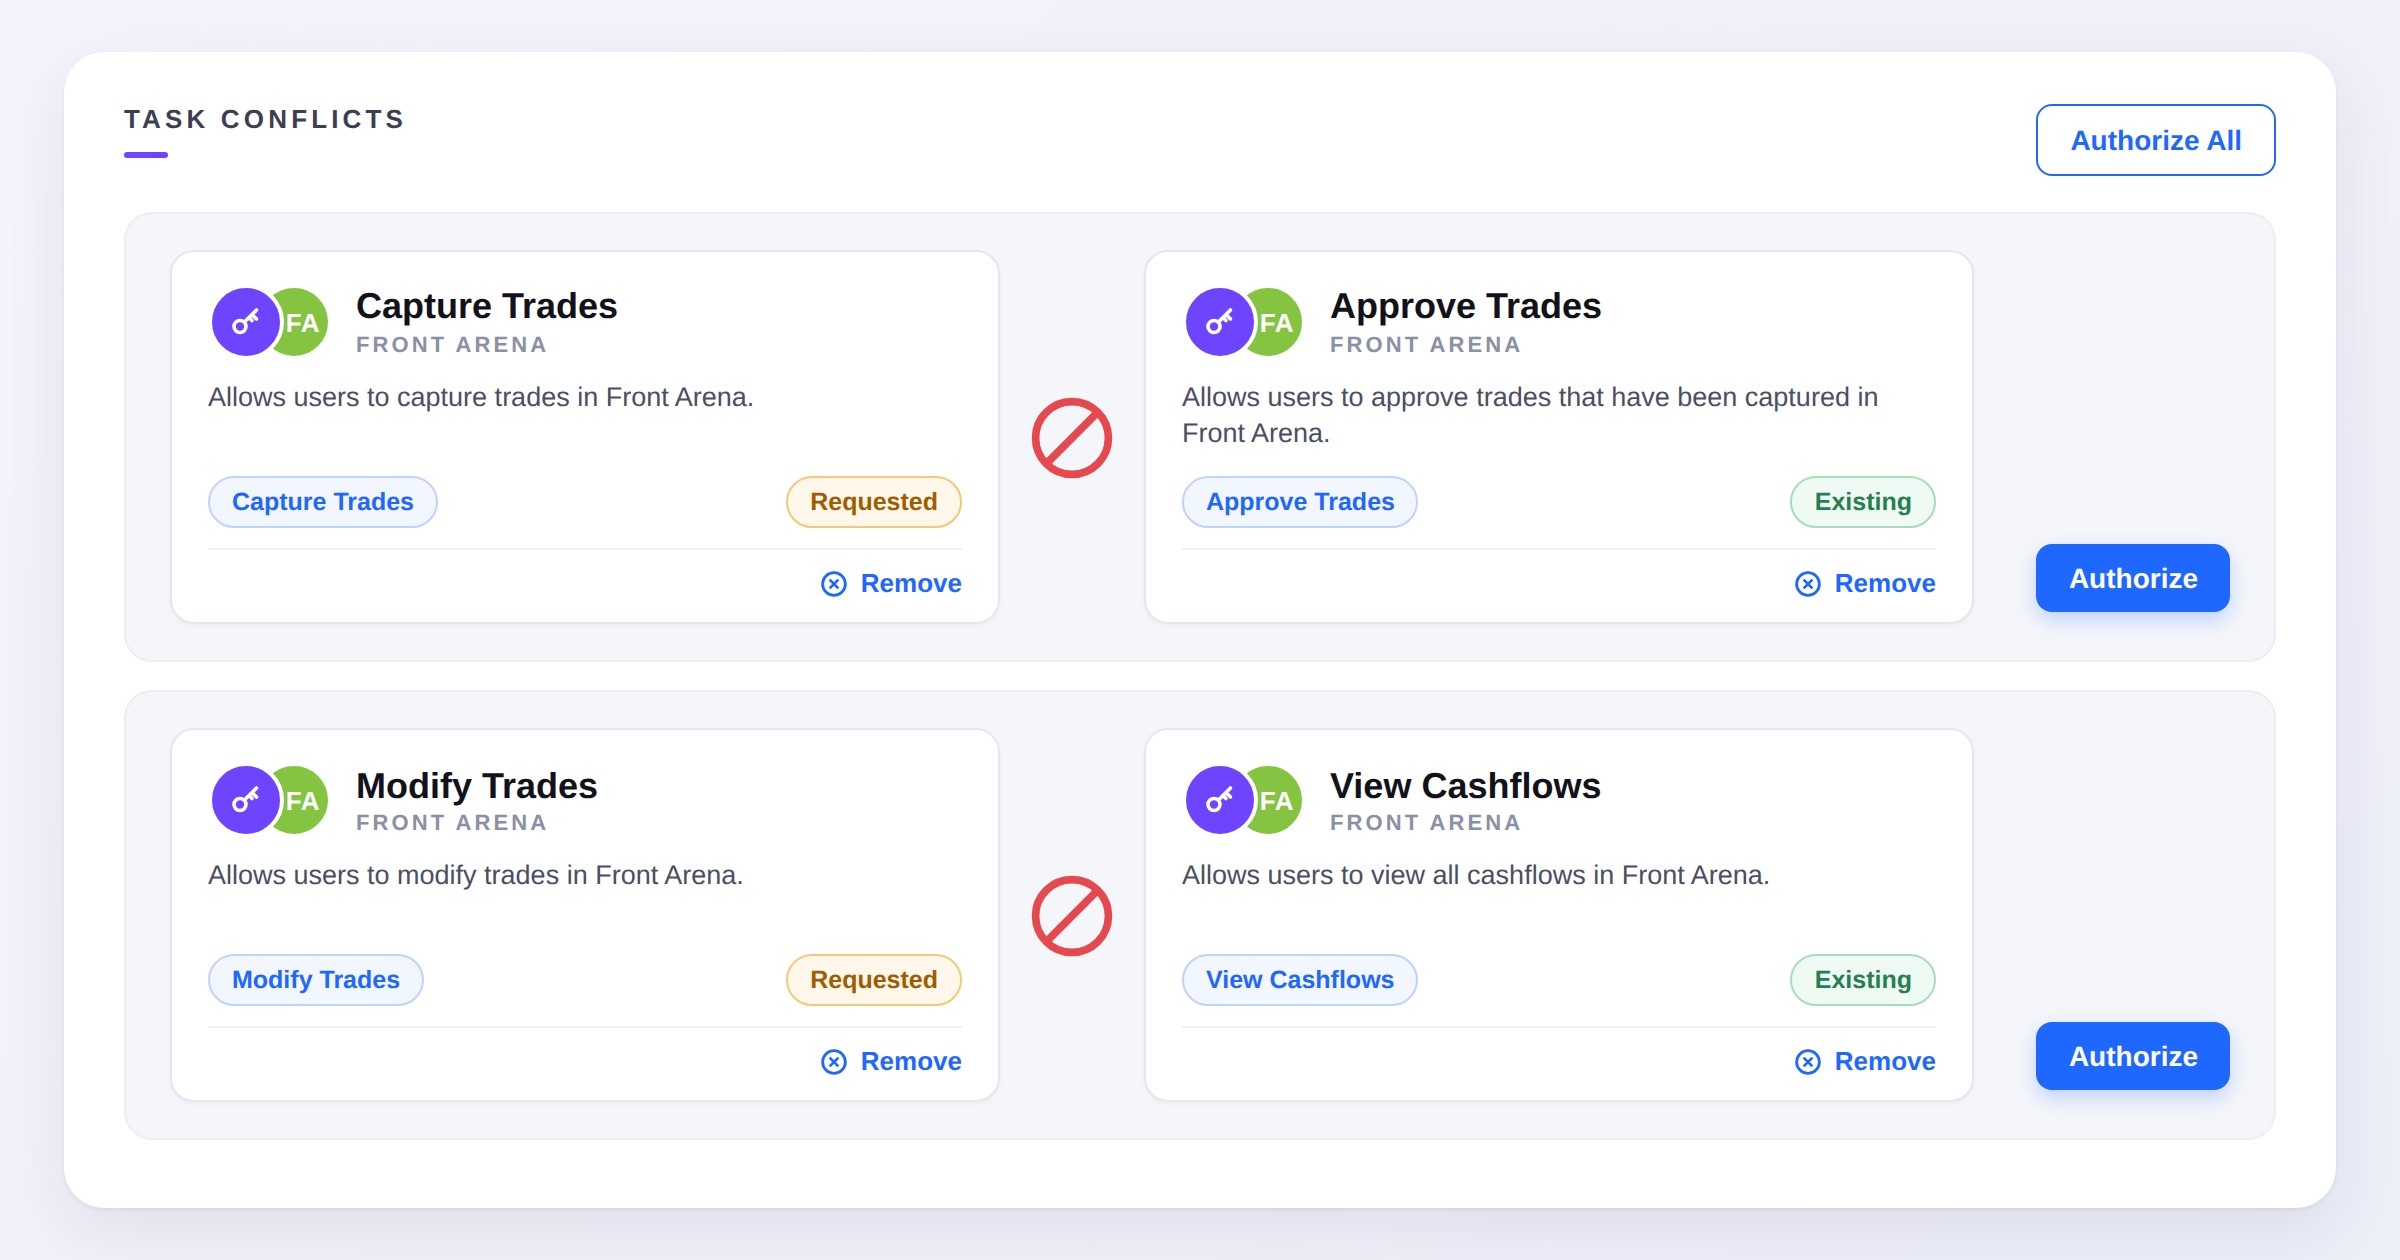
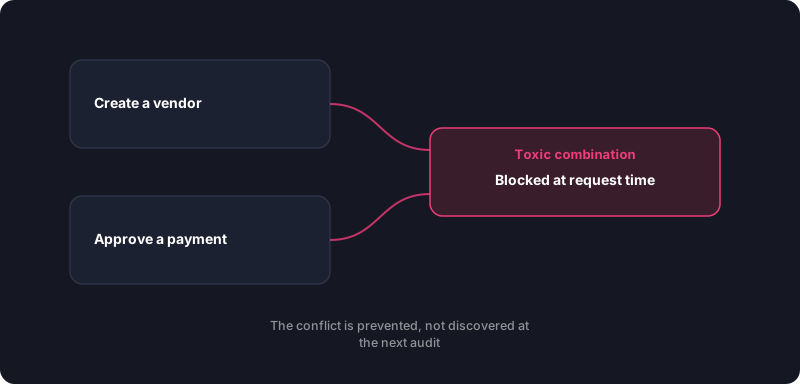
Automatic detection of toxic combinations
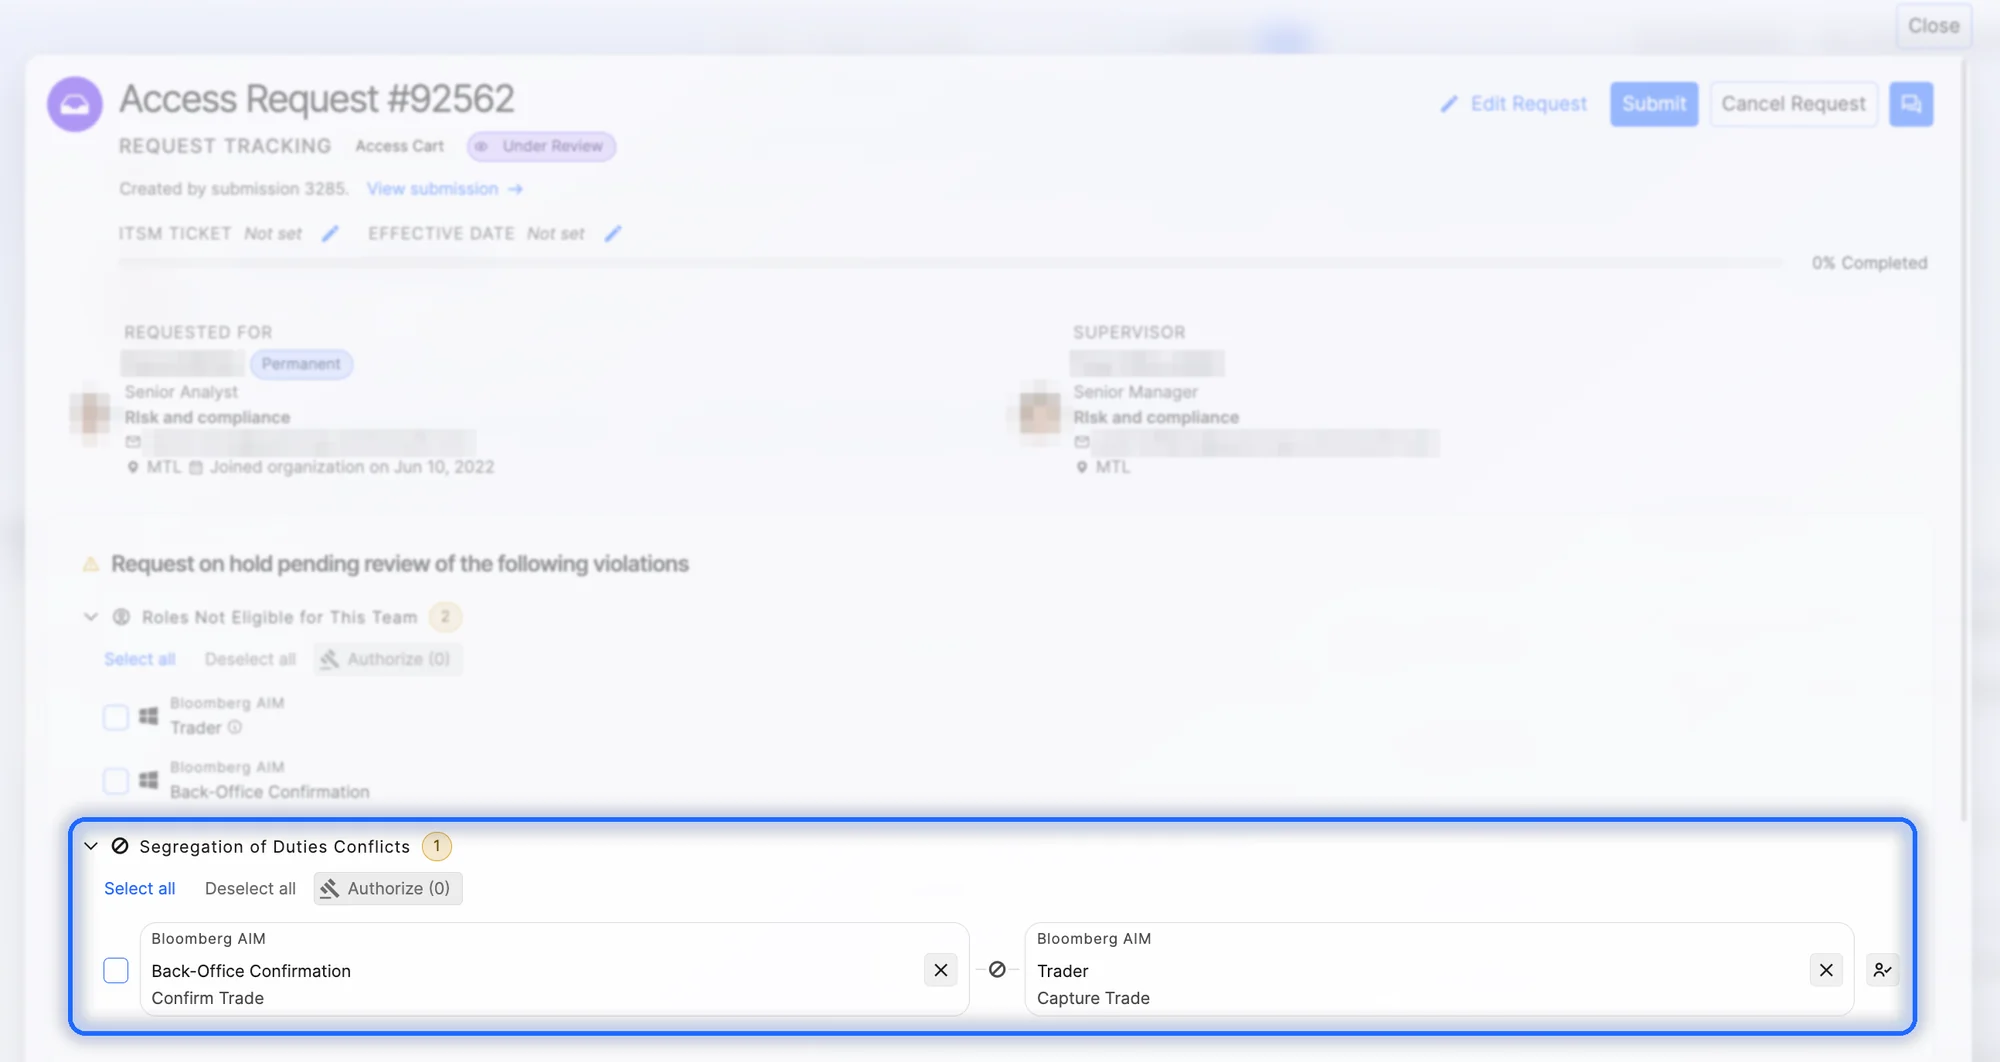
Automatic detection of toxic access combinations, so a Segregation of Duties conflict is blocked at the point of request rather than discovered at the next audit.
- Conflicts evaluated before access is granted, not after.
- Existing toxic pairs surfaced across the current population.
- Trailing permissions from role changes systematically eliminated.
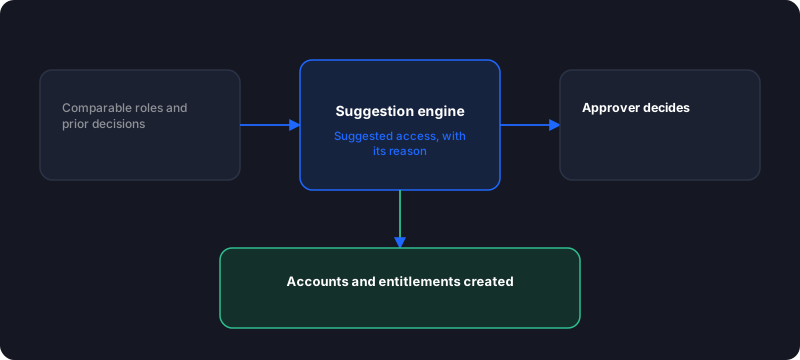
Access suggestion engine
An access suggestion engine and automated provisioning of accounts and entitlements, so the common case resolves without a human in the loop.
- Suggestions drawn from comparable roles and prior decisions.
- Automated provisioning of accounts and access on approval.
- Approvers see why a request was suggested before they decide.
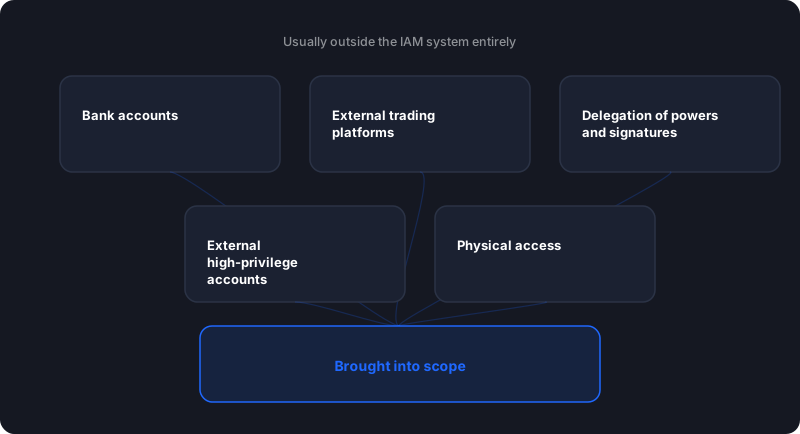
Financial and external access
Management of access to bank accounts, external trading platforms, and the delegation of powers and signatures — the high-consequence access that usually sits outside the IAM system entirely.
- Bank accounts and external trading platforms brought into scope.
- Delegation of powers and signatures tracked as entitlements.
- External accounts with high privileges, and physical access.
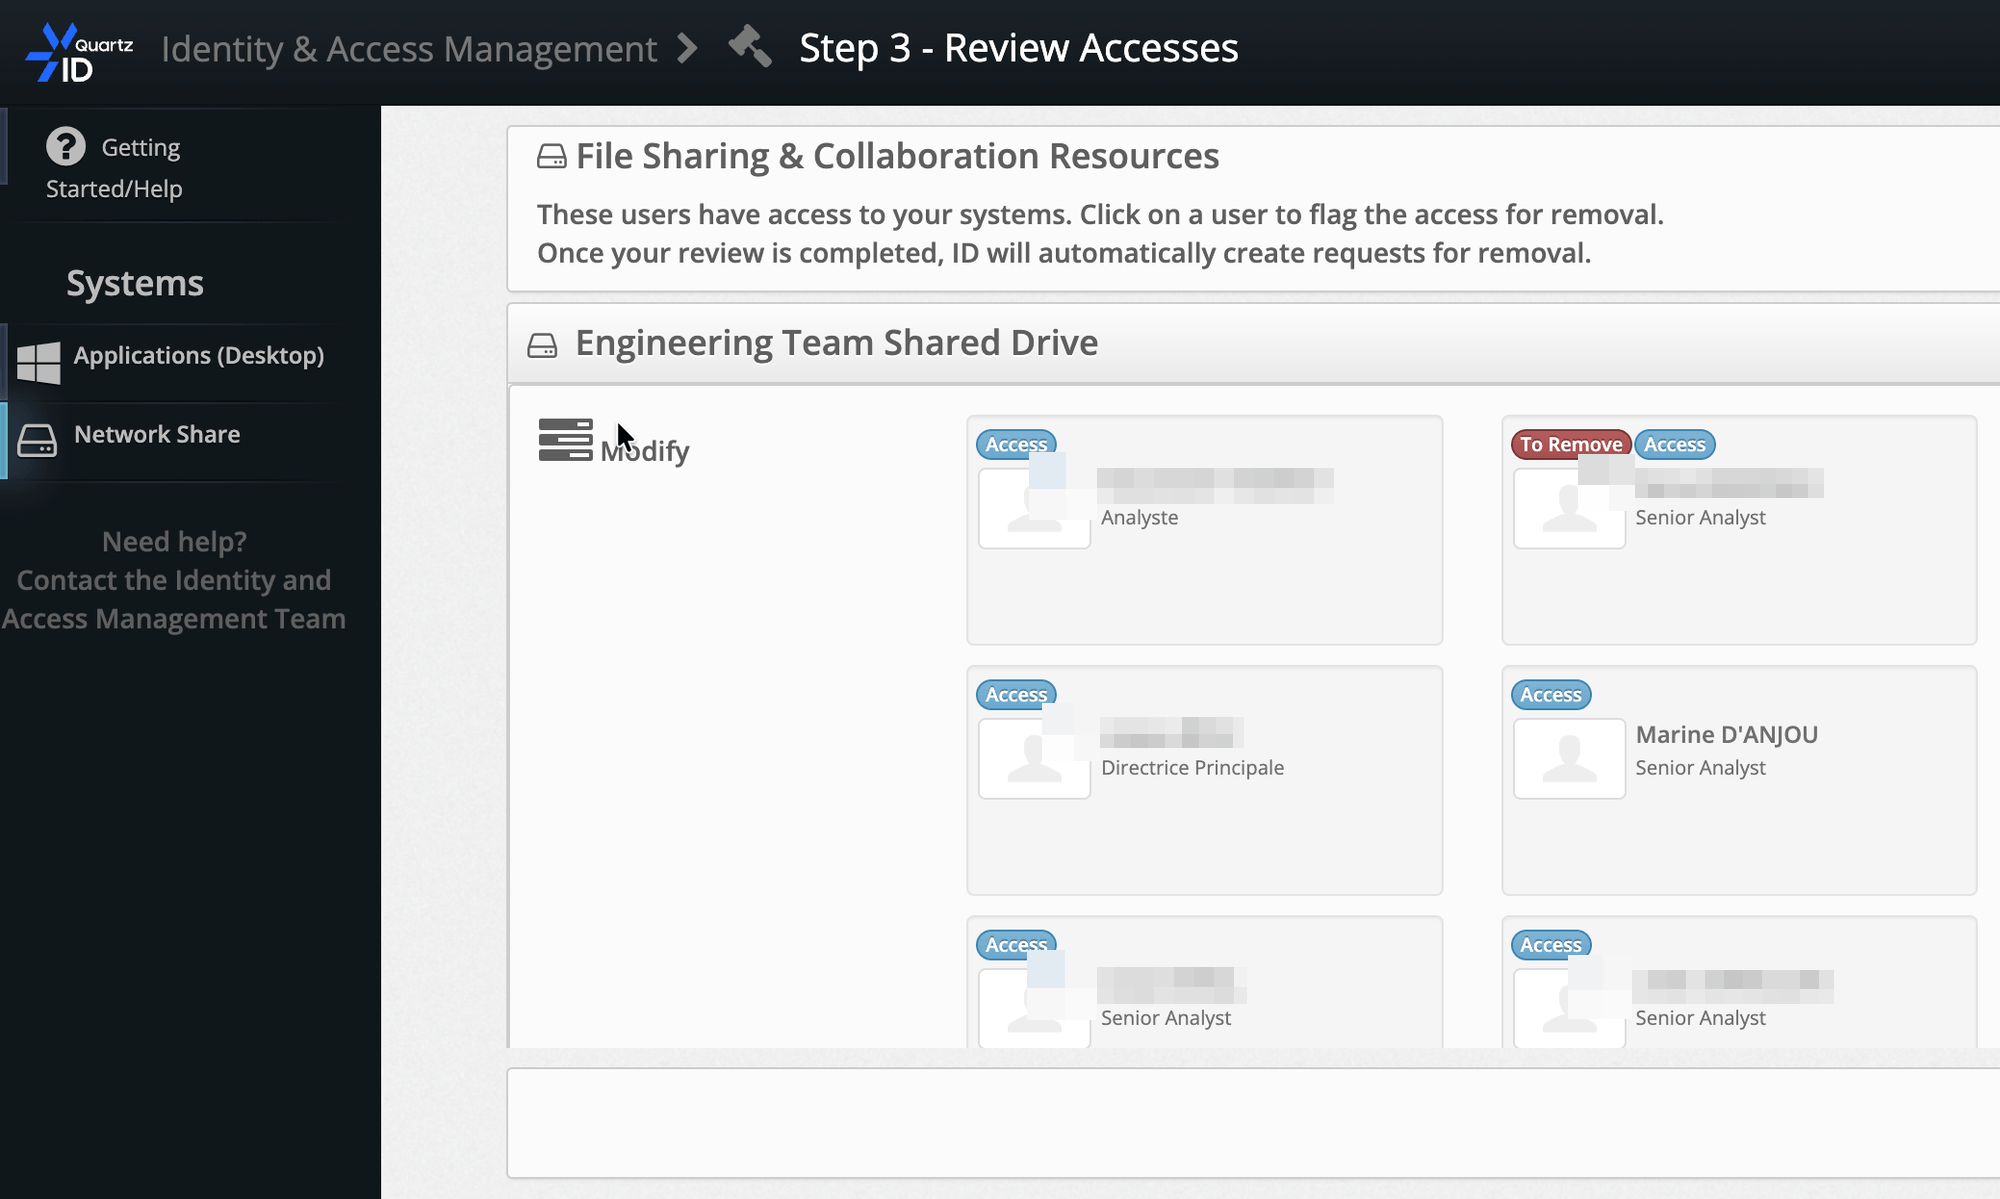
Periodic access reviews
Periodic access reviews of authorisations with consolidated reporting, a complete audit trail and SLA management, so a review campaign produces evidence rather than a spreadsheet.
- Campaigns scoped by application, population or risk.
- Consolidated reporting across every campaign.
- Complete audit trail retained as evidence.
Segregation of duties
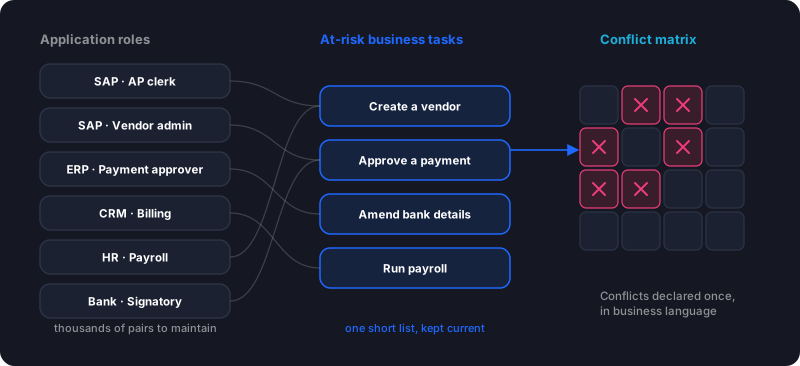
Map roles to business tasks, not to each other
Maintaining toxic permission pairs is where most IAM programmes stall: thousands of permission pairs across thousands of applications have to be analysed and flagged application-role by application-role. That is rarely sustainable, and until it is done a platform cannot reliably block or detect an SoD conflict at all.
- Map to a short list of at-risk business tasksClients map application roles to a customisable set of business tasks, rather than to every other role.
- Conflicts declared once, in business languageA limited number of understandable task pairs are flagged in a conflict matrix, and every role mapped to them inherits the rule.
- Replacing an application stops being a re-analysisMap the new application’s roles to the tasks they support and they are automatically flagged against every conflicting role — saving countless hours of analysis and configuration.
Continuous control
Your rules and processes applied systematically, anytime, anywhere
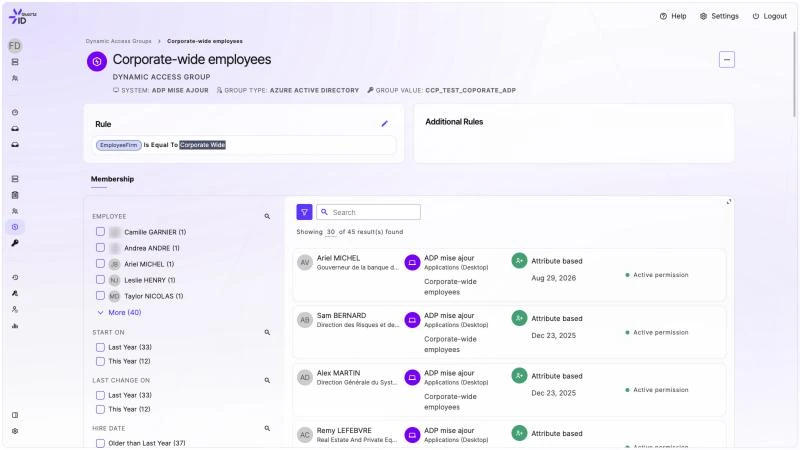
Permanent compliance with internal and external rules, real-time alerting when a risk materialises, and resolution driven by the people closest to the risk.
- Real-time automated alertingRaised the moment a rule or process is violated, not at the next review.
- Crowdsourced alert managementAlerts are parameterised and managed by the business, with a catalogue of rules covering every department.
- Workflows that match the alertAssignment and remediation routed by severity, SLA and skills, with tracking and notification wherever you are.
Why Choose QuartzID?
Explore the QuartzID solutions
Six solutions covering the identity and access governance programme end to end.
Identity Governance & Compliance
Centrally enforce least privilege, automate access reviews, and prove compliance instantly.
ExploreAutomated Identity Lifecycle
Onboard, move, and offboard users in minutes with zero-touch provisioning and deprovisioning.
ExploreAccess Certification & Recertification
Make access reviews fast, accurate, and painless for managers and application owners.
ExploreIntelligent Access Request & Approval
Empower users with an intuitive access request portal backed by policy, risk, and AI-driven approvals.
ExploreModern Authorization & Policy Management
Replace static groups and ACLs with attribute-based, context-aware authorization policies enforced everywhere.
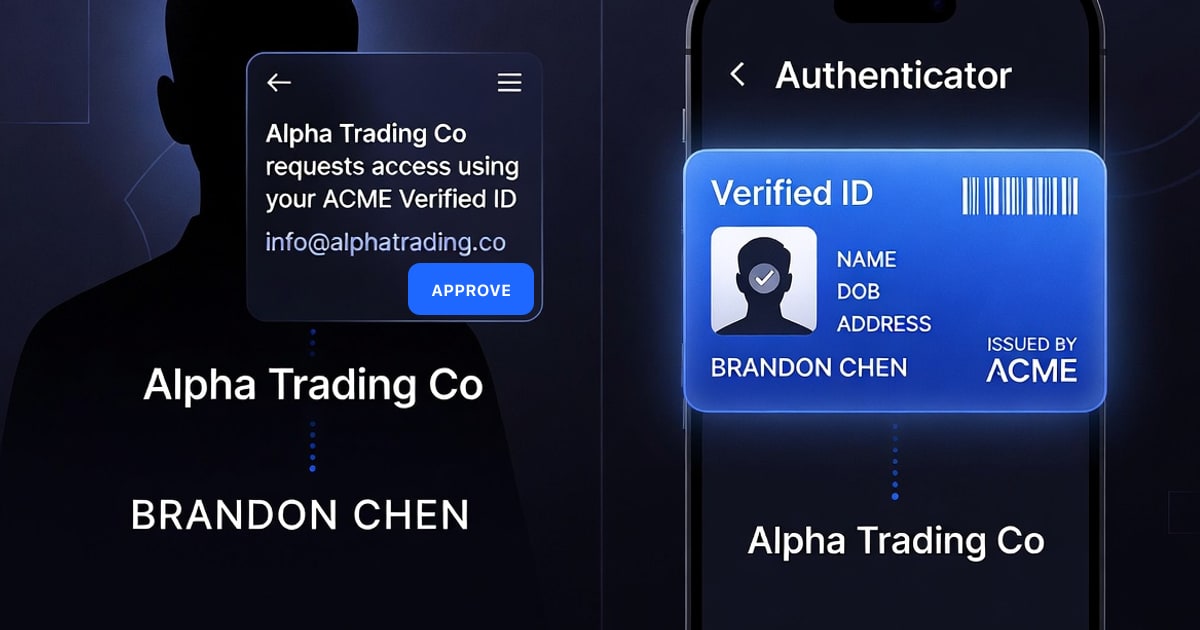
ExploreVerified ID for B2B Collaboration
Let consultants, partners, and vendors prove who they are using credentials their employer already issued. Grant precise access in seconds — and automatically revoke everything the moment that credential is no longer valid.
ExploreEase of implementation is at the heart of our solution
QuartzID can be quickly and progressively onboarded, so it starts delivering a return before the programme is finished.
No-code configuration
A fully configurable console — implementation is configuration, not development.
Seamless onboarding
Onboard progressively, application by application, rather than in one cutover.
Plug-and-play automation
ITSM synchronisation and integration toolkits for the systems you already run.
Security at the heart of the architecture
SOC-2 Type II certified, and available on the Microsoft Azure Marketplace.
What changes when IAM starts from business risk
Core platform strengths
Dedicated tenants
One client, one tenant. No shared data plane.
Hosting flexibility
Public cloud, private cloud, or on-premise.
Standards compliant
SOC-2 Type II, PIPEDA and GDPR compliant.
Flexible authentication
SAML, OAuth 2, Entra ID, Active Directory, Auth0 and MFA.
Cognitive search
Every object is indexed, so anything is one search away.
Notifications done right
Push, email, web and desktop, on a queue built to stay up.
Frequently asked questions
Trusted by
Ready to Transform Your IAM?
Experience the QuartzID difference and secure your business today with our risk-centric approach.
Or contact us directly: +1 888.526.1830
Latest Insights
Stay updated with our latest articles and insights