
Modern Authorization & Policy Management
Replace static groups and ACLs with attribute-based, context-aware authorization policies enforced everywhere.
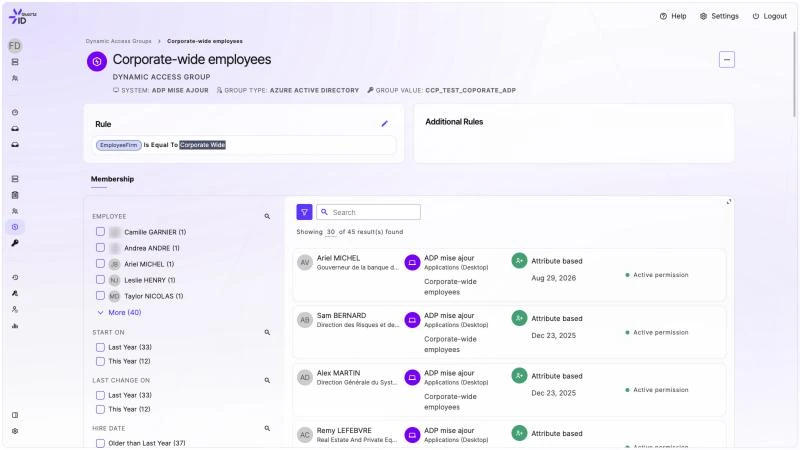
Beyond Groups: Dynamic Policy
Sound Familiar?
Common challenges that organizations face
Beyond Groups: Dynamic Policy
Static AD/LDAP groups and manual ACLs can't keep up with today's dynamic workforce and cloud applications. Our policy-as-code engine lets you define fine-grained authorization rules using identity attributes, device posture, location, time, and risk signals.
Policies are centrally managed but enforced natively across SaaS, custom apps, d
Policies are centrally managed but enforced natively across SaaS, custom apps, data lakes, and cloud infrastructure—no agents required. Achieve true Zero Trust without ripping and replacing existing systems.
How QuartzID Transforms Your Modern Authorization & Policy Management
Powerful capabilities to modernize your operations
Trusted by Risk Leaders Worldwide
The organizations that trust us with their risk programme
Key Benefits
Discover how our Modern Authorization & Policy Management solution can transform your business
Attribute-Based Access Control (ABAC) / Policy-as-Code
Define fine-grained authorization policies using attributes, roles, and context in a flexible policy language.
Context-aware policies (location, device, time, risk)
Enforce dynamic access decisions based on user location, device trust, time of day, and real-time risk scores.
Native enforcement in AWS, Azure, GCP, Snowflake, custom APIs
Policies are enforced directly in your cloud platforms and applications without requiring agents or middleware.
Key Features
Explore the powerful capabilities of our Modern Authorization & Policy Management solution
Attribute-Based Access Control (ABAC) / Policy-as-Code
Define fine-grained authorization policies using attributes, roles, and context in a flexible policy language.
Context-aware policies (location, device, time, risk)
Enforce dynamic access decisions based on user location, device trust, time of day, and real-time risk scores.
Native enforcement in AWS, Azure, GCP, Snowflake, custom APIs
Policies are enforced directly in your cloud platforms and applications without requiring agents or middleware.
Centralized policy lifecycle & version control
Manage all authorization policies from one place with full version history, rollback, and testing capabilities.
Ready to transform your modern authorization & policy management?
Schedule a personalized demo to see how our solution can address your specific challenges.
Security and compliance
- SOC 2 Type IIAudited by Sensiba LLP.
- ISO/IEC 27001Certified by Sensiba LLP, an ANAB-accredited certification body.
- GDPRCompliant with the EU General Data Protection Regulation.
- PIPEDAReady for Canada's Personal Information Protection and Electronic Documents Act.
Reports available upon request