Partner & consultant access
One verified ID. Zero friction. Instant trust.
Let consultants, partners and vendors prove who they are using credentials their employer already issued. Grant precise access in seconds — and automatically revoke everything the moment that credential is no longer valid.
Kira needs Brandon in by Friday. By Monday he might be gone.
This is how modern B2B collaboration actually works — and why traditional guest accounts fail.
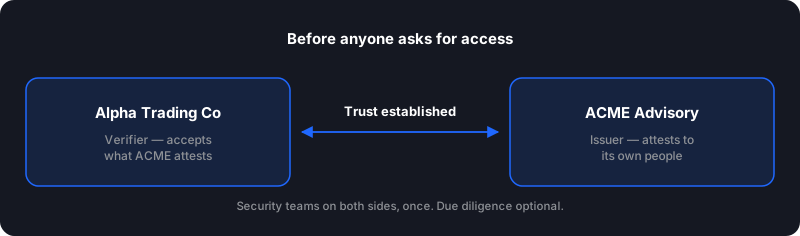
Alpha Trading Co, a global investment firm, regularly works with ACME Advisory on high-stakes M&A deals. Security teams at both companies completed due diligence and established a formal trust relationship in QuartzPass.
Kira needs Brandon, a senior manager at ACME, in Alpha’s deal room, financial models and internal channels for the next six weeks. Brandon has never worked with Alpha before. There is no guest account — and there does not need to be one.
Brandon presents the credential ACME already issued him, containing his name, title and employment status. He is in, with the right role and deal-specific access, in under a minute. No password. No ticket. And the moment he leaves ACME, he disappears from Alpha.
The trust comes first
Two security teams agree, once, that each will accept credentials the other issues. Nothing in that agreement concerns any individual — it is what makes every later request cheap.
How it works
Four parties. One source of truth. Zero standing risk.
Establish trust
Security teams at both organizations mutually approve a trust relationship inside QuartzPass, with an optional due-diligence workflow.
Request external access
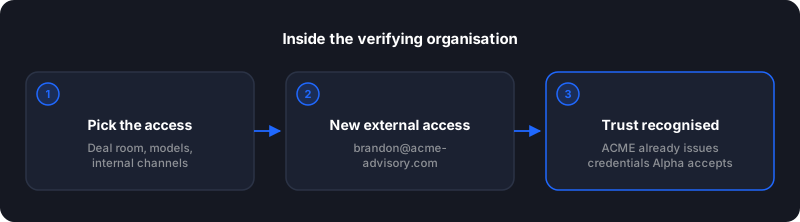
Any authorized internal user selects “New external access” and enters the partner’s corporate email. QuartzPass instantly recognizes the trust.
Present the credential
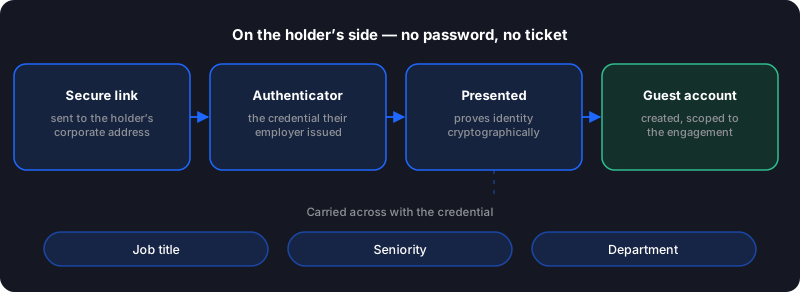
The external user receives a secure link and presents their employer-issued credential — authenticator app, wallet or corporate IDP — to cryptographically prove identity and claims.
Continuous validation
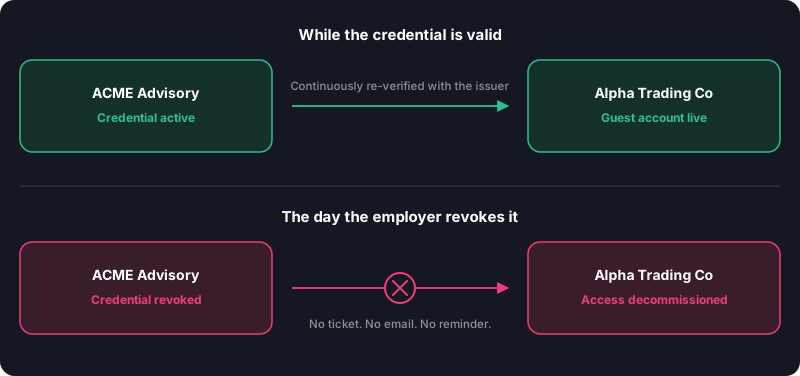
QuartzPass regularly verifies the credential is still active with the issuing organization. Revocation at source means instant, automatic decommissioning at every relying party.
Requesting access, without contacting anyone
An authorized internal user picks the access and enters the partner’s corporate address. The platform recognises a domain it already trusts. No ticket, and nobody at the partner is asked to confirm employment.
Proving it, and what travels with the proof
The external user presents the credential their employer already issued. Job title, seniority and department arrive as assertions from the organisation that employs them — not as fields somebody typed into a form.
And the day it is revoked
The credential is re-verified with the issuer on a cycle rather than remembered. When the answer changes, the guest identity and every permission derived from it go with it.
Capabilities that change how you work with the outside world
Not just another guest account. A living, verifiable relationship.
Employer-issued claims
Pull verified attributes directly from the partner’s IDP — job title, seniority, department, clearance level, employee ID — without manual data entry or spreadsheets.
Continuous verification
QuartzPass does not rely on a one-time check. It continuously confirms the credential is still valid with the issuing organization.
Automatic decommissioning
When the external user’s credential is revoked at their employer, QuartzPass instantly withdraws their identity and every permission across connected systems.
Passwordless by design
No more shared passwords, no more “forgot password” tickets from consultants. They authenticate with the same strong credential their employer trusts.
Native IGA integration
Credential-verified guests are first-class identities in your governance, access reviews, SoD policies and lifecycle workflows — not a bolted-on afterthought.
Audit-grade evidence
Every verification, claim assertion and revocation event is immutably logged. Perfect for SOC 2, ISO 27001, financial services regulators and customer audits.
What you issue
The employer issues its people; the trust relationship between the two organizations is a credential too — the same mechanism a trust list uses, one partner at a time.
- Person
Verified Employee
VALIDClaims
- Given name
- Job title
- Employment status
- Person
Verified Contractor
VALIDClaims
- Sponsoring organization
- Engagement end date
- Role
- Organization
Trusted Partner Organization
VALIDClaims
- Legal name
- Verified domain
- Trust relationship since
Your systems ask. QuartzPass answers. Revocation reaches everywhere.
People
- 1Your IAM/IGA onboards an external user and raises a verification request
- 2The person presents the credential their employer issued
- 3Verified attributes are written back (SCIM); the signed result arrives by webhook
- 4Access and role are granted — and withdrawn everywhere the moment the employer revokes
Organizations
- 1Your procurement or vendor system calls the API before a step completes
- 2QuartzPass confirms the supplier’s badge against the authority’s list
- 3The step closes with the verification recorded
- 4Your system subscribes to revocation events for that supplier
Revocation reaches every connected system
- QuartzID· native
- Microsoft Entra ID
- Okta
- SailPoint
- Saviynt
- Ping
- Procurement and vendor platforms via API
Protocols: SCIM · SAML · OIDC · REST · webhooks
QuartzPass issues and verifies. Your identity platform decides what it unlocks.
Works with what you already run
QuartzPass issues and verifies the credential. Your identity platform decides what it unlocks — whichever platform that is.
Native with QuartzID
QuartzID consumes QuartzPass credentials directly, so verified externals land inside the same governance, access reviews and lifecycle workflows as everyone else.
Open standards, not lock-in
Built on W3C Verifiable Credentials, OpenID for Verifiable Credentials (OID4VCI / OID4VP) and SD-JWT; ISO/IEC 18013 mdoc in development. Any conformant wallet or issuer interoperates — no proprietary bridge required.
Any IGA or IAM platform
Entra ID, Okta, SailPoint, Saviynt, Ping and the rest integrate through SCIM, SAML, OIDC and REST. QuartzPass sits alongside what you have rather than replacing it.
Verified credentials vs traditional guest accounts
What changes
Founding Members — 50% off for life
Every plan starts with a 90-day free trial from your first billable usage. Plans signed before June 30, 2027 keep 50% off list for life. Verifying is free, always.
Built for the way modern enterprises actually collaborate
Pricing
What it costs
A 400-person consulting firm issuing Verified Employee to everyone pays the Issuer fee plus usage; every relying party verifies for free.
See pricingUsually on Issuer
A 400-person consulting firm issuing Verified Employee to everyone
$70 / month in usage
plus the $15/mo Issuer fee
90 days free from your first billable credential
Questions
Ready to replace guest accounts with real trust?
See how QuartzPass works with your identity providers and partner ecosystem.
Typically live in production within 6–8 weeks.