
Internal Control & Audit
Document, test and certify controls, run audit missions against them, and track every recommendation through to evidenced closure.
Every control documented against the perimeter that owns it and the risks it covers, so a risk-and-control matrix means something and its gaps are visible.
Sound Familiar?
Common challenges that organizations face
Evidence is collected once a year
Control testing is a point-in-time exercise. Between two campaigns, nothing is observed and nothing is proven.
Findings outlive the fix
Recommendations and action plans are tracked in email and slide decks, so closure is asserted rather than evidenced.
Exceptions surface at the next campaign
Without automated controls running against live data, an exception is found when someone next goes looking rather than when it happens.
The audit trail is not attached to anything
Alerts, tasks and observations scatter across mailboxes instead of accumulating against the perimeter, which is the evidence an auditor asks for.
How QuartzIQ Transforms Your Internal Control & Audit
Powerful capabilities to modernize your operations
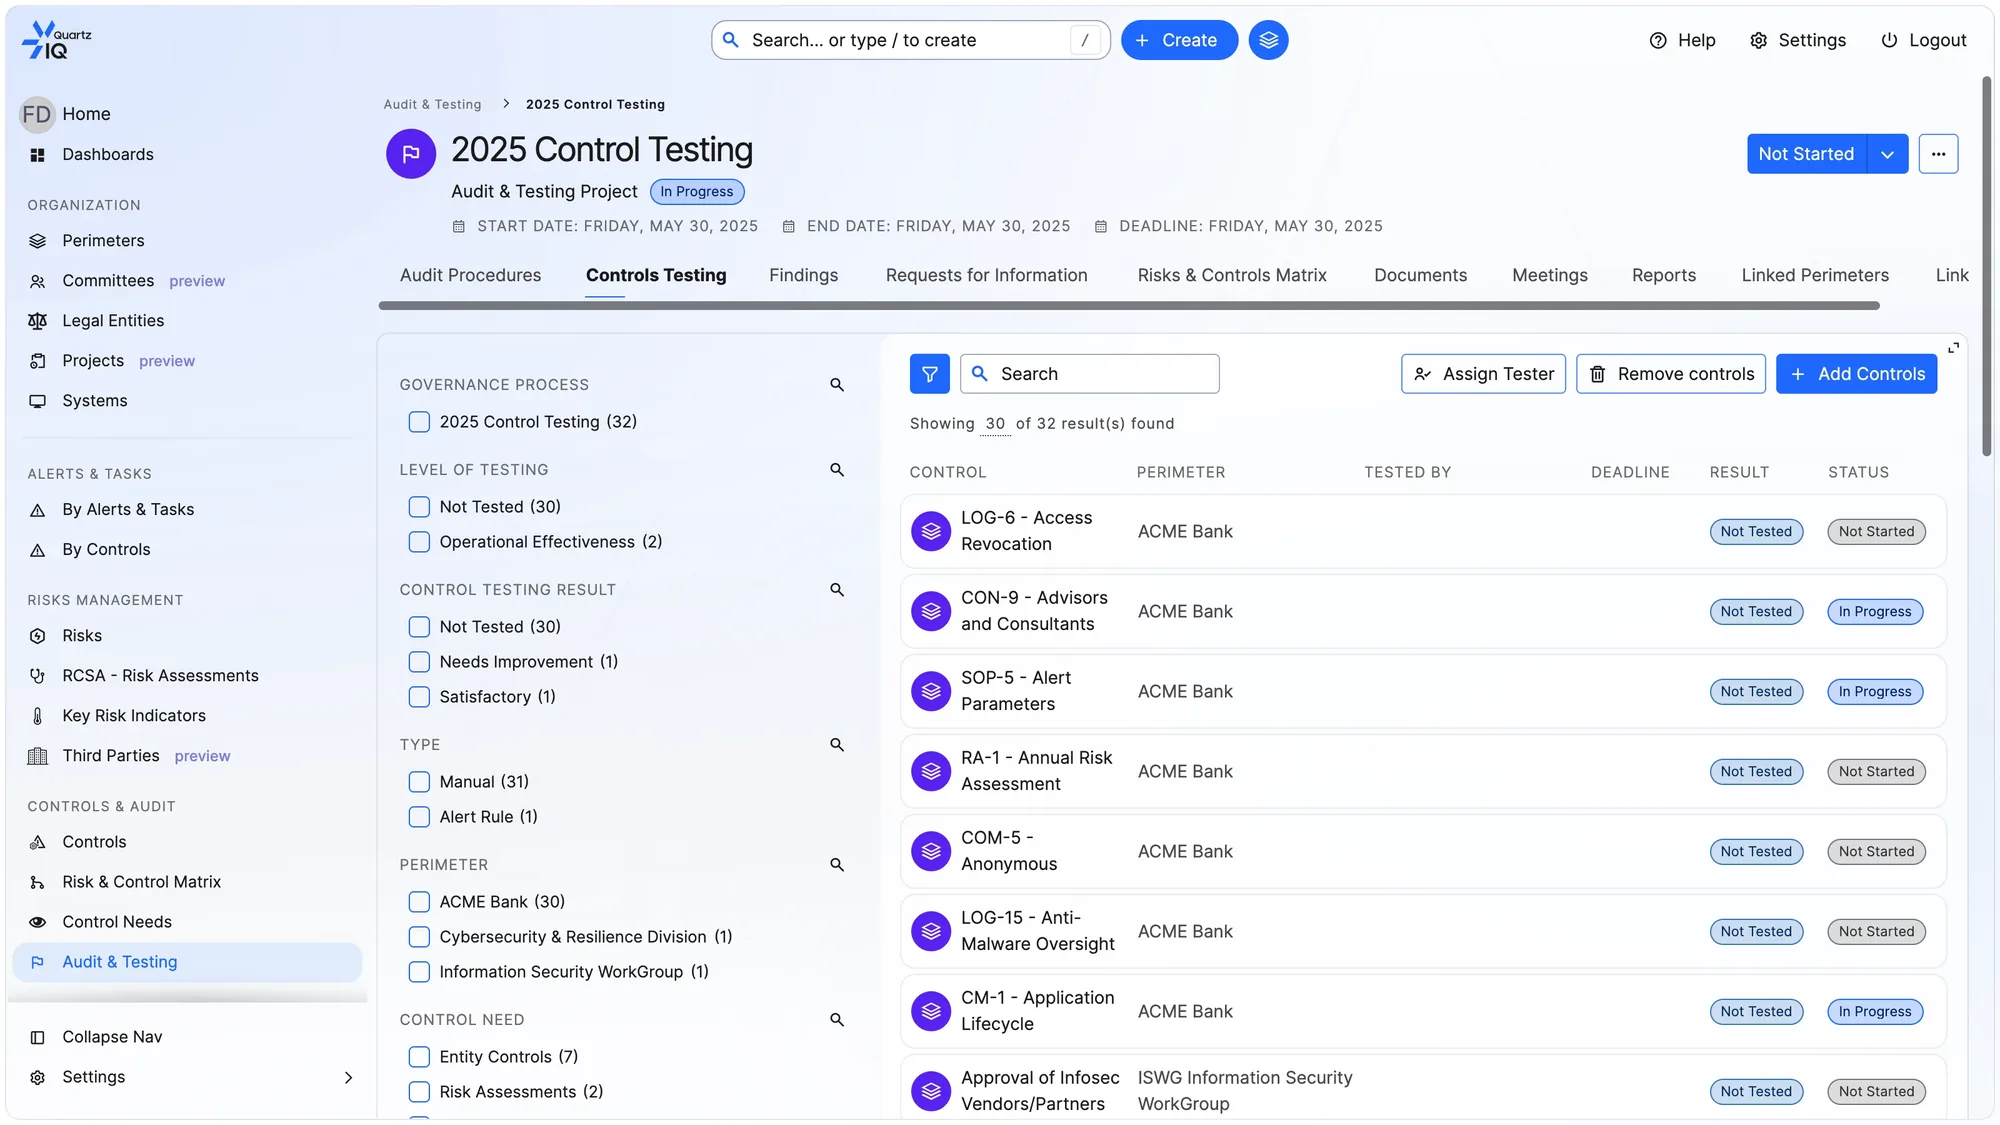
Control documentation and inventory
Document every control as it exists today — manual, automated, semi-automated, checklist or committee — against the hierarchical perimeter that owns it and the risks it covers.
Tailored for Your Challenges
Explore specific applications of our Internal Control & Audit solution
Trusted by Risk Leaders Worldwide
The organizations that trust us with their risk programme
Key Benefits
Discover how our Internal Control & Audit solution can transform your business
Evidence between campaigns
Automated controls observe continuously, so the period between two testing campaigns stops being a blind spot.
Findings closed, not asserted
Recommendations and action plans are tracked against the control and the perimeter they came from, so closure carries its own evidence.
Gaps the matrix finds for you
The risk and control matrix suggests where coverage is missing from your own data, instead of leaving it to be noticed at the next review.
Key Features
Explore the powerful capabilities of our Internal Control & Audit solution
Control Documentation and Inventory
Document all your controls and your governance using hierarchical and overlapping perimeters.
Control Testing and Certification
Integrated management of control testing campaigns (second line of defence), evaluation and certification of controls.
Control Programmes
Creation of customised control programmes and monitoring of their deployment throughout your perimeters.
Internal Audit Missions
Creation and management of internal audit assignments.
Recommendations and Action Plans
Creation of recommendations and tracking of action plans implemented throughout the organisation.
Execution, Alerts and Tasks
Generate and assign control tasks, and monitor execution.
Automated Continuous Controls and Continuous Auditing
Set up automated controls using your data for continuous monitoring and auditing.
Customisable Detection Thresholds
Fully customisable rule detection thresholds, set by business teams through an intuitive interface.
Control Catalogue for Fraud Detection
A library of ready-to-use controls for continuous monitoring and fraud detection, suitable for all industries.
Real-time Alert Detection
Real-time alerts in the event of potential fraud, error or process violation, determined according to your rules.
Artificial Intelligence
Artificial intelligence integrated into the application to create and improve your rules.
Ready to transform your internal control & audit?
Schedule a personalized demo to see how our solution can address your specific challenges.
Security and compliance
- SOC 2 Type IIAudited by Sensiba LLP.
- ISO/IEC 27001Certified by Sensiba LLP, an ANAB-accredited certification body.
- GDPRCompliant with the EU General Data Protection Regulation.
- PIPEDAReady for Canada's Personal Information Protection and Electronic Documents Act.
Reports available upon request